MEV Scams in DeFi (2026): Types, Red Flags, and How to Avoid Them
Protective guide to MEV scams: fake bots, approval honeypots, sandwich losses vs wallet drains, and a 2026 mitigation checklist.
Protective guide to MEV scams: fake bots, approval honeypots, sandwich losses vs wallet drains, and a 2026 mitigation checklist.

I build DeFi analytics at Crypticorn. I do not run an MEV bot, and I have watched friends lose funds to "guaranteed arbitrage" Telegram scripts that were just wallet drains. This page separates adversarial MEV on swaps from actual scams (fake bots, approval honeypots, key theft) and lists mitigations that still work in 2026.
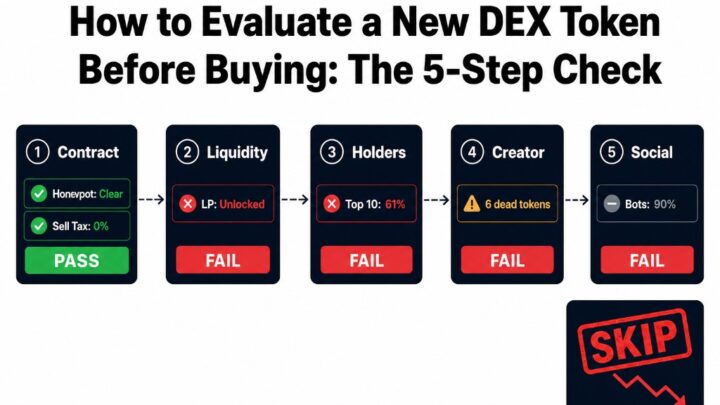
For how legitimate MEV bots extract value on-chain, read what MEV bots are and who pays. For pre-trade token safety before you sign anything, see how to evaluate a new DEX token.
Last updated: August 2026. Not financial advice. See our disclaimer.
MEV scams in DeFi usually mean one of three things: (1) fake MEV bot products that steal deposits, private keys, or unlimited token approvals; (2) counter-MEV honeypots that bait automated bots into approving malicious contracts; or (3) marketing that labels normal sandwich losses on public mempool swaps as a "scam" without explaining mechanics. Sandwiching is adversarial and costly, but it is not the same as a wallet drain. Avoiding real scams means tight approvals, verified contracts, private transaction submission where appropriate, and skepticism toward passive-income bot ads.
| Category | What happens | Typical victim | What helps |
|---|---|---|---|
| Sandwich / frontrun on public swap | Searcher wraps your trade for extractable slippage | Retail swappers on public mempool routes | Tight slippage, smaller size, Flashbots Protect or wallet private send |
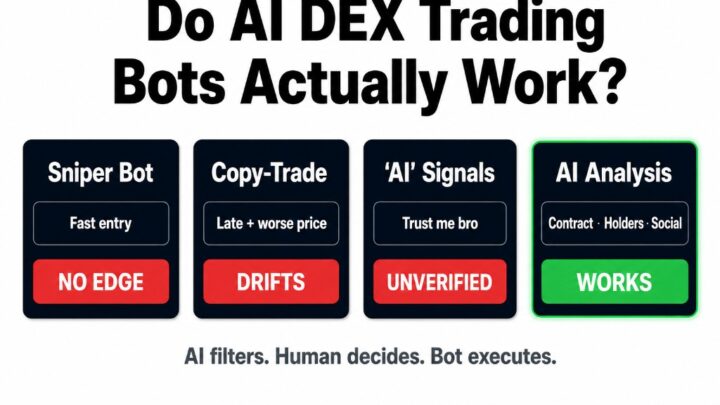
| Fake MEV / arbitrage bot | Deposit or API key harvest; backtest theater | Users chasing passive income ads | Treat as fraud until audited; burner wallet only; see do AI DEX bots actually work |
| Approval honeypot | Profitable-looking trade leaves standing allowance; later sweep | Automated bots and approval-heavy wallets | Exact approvals, revoke cadence, block flagged contracts at signing |
| Malicious "anti-MEV" download | Fake installer, clipboard hijack, drainer site | Telegram / YouTube funnel traffic | Official repos only; hardware wallet; no seed entry in browser tools |
| Phishing RPC / wallet connect | Spoofed interface signs transfer or setApprovalForAll | Users rushing new meme launches | Bookmark official apps; read simulation preview; slow down |
Maximal extractable value (MEV) is profit available from transaction ordering within a block. Searchers run bots that monitor pending swaps. A classic sandwich buys before your trade, lets your trade move price, then sells after.

You lose mainly through worse execution price and extra slippage, not because someone stole your wallet keys. Mitigation is execution hygiene: lower slippage tolerance, split large orders, use intent-based or protected routes where your wallet supports them, and accept that thin pools on new tokens are hostile territory.
Full math and who pays: MEV bots explainer.

These are off-chain fraud packages marketed as "ETH arbitrage bots" or "Solana MEV snipers." Common pattern:
No legitimate MEV operation needs your seed phrase. If setup requires exporting keys into a web panel, stop.
We cover sniper/MEV-adjacent automation honestly in sniper bot comparison and what sniper bots are. Spoiler: most retail "MEV bot" ads optimize for deposits, not searcher PnL.
In June 2026, the widely tracked JaredFromSubway MEV bot lost about $7.5M (roughly 4,424 ETH equivalent across WETH, USDC, and USDT) to a counter-MEV honeypot. Independent analyses (CertiK, Blockaid, thirdweb) describe the same mechanics: attackers deployed dozens of fake token and pool contracts that looked like profitable arbitrage venues. The bot granted token spending approvals during small "winning" interactions. Those approvals were not fully consumed or revoked. Later, the attacker swept balances in coordinated transactions.
Lesson for humans, not only bots: standing unlimited approvals are latent theft. A contract that looks fine on trade one can drain you on trade two.
Searchers also compete to liquidate undercollateralized lending positions on protocols like Aave. That is aggressive and can feel unfair if you get liquidated during a wick, but it is protocol-defined behavior, not a fake bot vendor. Risk here is position sizing and health factor, not downloading a drainer.
If you trade on-chain with leverage, monitor health factor and oracle latency. Do not confuse liquidation bots with Telegram "MEV bot" sellers.
Crypticorn does not sell mempool front-running software or Telegram entry packages. We build analytics for traders evaluating on-chain tokens: security cues, holder breakdown, social context, and chart review in DEX AI Trading. That is pre-trade risk reduction, not a promise to beat searchers.
If you want the honest DeFi + AI framing without bot hype, start with what decentralized AI trading is.
MEV scams are mostly signing problems dressed up as trading edge. Sandwich losses are real, but you address them with execution settings and route choice. Wallet drains and approval honeypots are the catastrophic category, and they keep working because people rush launches and trust screen-recorded PnL. Slow down at the wallet prompt. That is still the best anti-MEV tool retail has.
In common usage, an MEV scam is either a fraudulent product claiming guaranteed MEV profits, or an on-chain trap that steals funds via malicious contracts and token approvals. Sandwich losses on public swaps are MEV extraction, but they are a different problem from fake bot vendors or drainers.
On public blockchains, transaction reordering by searchers is generally part of open mempool competition, subject to local law and venue rules. Malicious off-chain products (fake bots, drainers, phishing) are fraud. Centralized exchanges prohibit insider-style front-running under their own terms.
Most fake bots ask for wallet connection, malicious contract deployment, or unlimited token approvals, then transfer assets to attacker addresses. Some collect upfront "activation fees" and never execute trades.
Use tight slippage limits, avoid oversized swaps in thin pools, split orders, and use protected/private transaction routes where available. Flashbots Protect is a widely used Ethereum option for reducing public mempool exposure.
In June 2026, the JaredFromSubway automated MEV bot lost about $7.5M to a counter-MEV honeypot that used fake tokens and pools to accumulate token approvals, then swept balances. Security firms documented approval hijacking as the core flaw.
No. Crypticorn provides DEX analytics and AI-assisted token review. We do not offer mempool front-running bots or guaranteed arbitrage automation.
Treat them as high risk by default. Verify open-source code, team identity, and on-chain track record. If the channel pushes urgency, unlimited approvals, or seed phrase entry, assume scam.